Connecting AI assistants with OAuth
You can connect an AI assistant to your Oneleet workspace by signing in with your Oneleet account. There are no keys to create or paste: add the Oneleet MCP server to your assistant, and it opens a browser window where you log in to Oneleet, review what the assistant is asking for, and pick the workspace it should work in.
Once connected, the assistant acts as you. It can only see and do what your own role in the workspace allows, and every action is attributed to your account. Your membership and role are checked on every call: if your workspace access is removed but you stay in the workspace as an employee, the assistant is limited to what an employee can do, and once you’re no longer a member of the workspace at all, the connection stops working.
What you need
Section titled “What you need”- A Oneleet account that is a member of at least one workspace. Any member can connect — no admin involvement is required — but what the assistant can do is limited by that member’s role.
- An MCP client that supports OAuth sign-in for remote MCP servers.
Oneleet supports the following clients:
| Client | How to connect |
|---|---|
| Claude (web, desktop, and mobile) | Add Oneleet from Claude’s connector directory (see Claude) |
| Claude Code | claude mcp add + /mcp → Authenticate — see Claude Code |
| ChatGPT | Add Oneleet from ChatGPT’s plugin directory (see ChatGPT) |
| Codex (CLI and IDE extension) | codex mcp add + codex mcp login — see Codex |
| Cursor | Add to mcp.json, then Connect — see Cursor |
| Devin (app.devin.ai) | Add a custom MCP with Oneleet’s client ID, then Connect (see Devin) |
| Google Antigravity | Add the server URL, then sign in — see Google Antigravity |
| Grok (grok.com) | Add a custom connector, then sign in — see Grok |
| Other clients without OAuth sign-in | Use a service key instead |
The Oneleet MCP server URL is the same for every client:
https://api.oneleet.com/mcpConnecting your assistant
Section titled “Connecting your assistant”Each client has its own way of adding an MCP server, but the sign-in part in the browser is identical — it’s described once in The sign-in flow below.
Claude
Section titled “Claude”Oneleet is listed in Claude’s connector directory, so you can add it to Claude on the web, Claude Desktop, and the Claude mobile apps without entering a server URL. Add it once and it’s available everywhere you use Claude.
-
Open Oneleet in Claude’s connector directory. You can also find it in Claude under Settings → Connectors by clicking Browse connectors and searching for
Oneleet.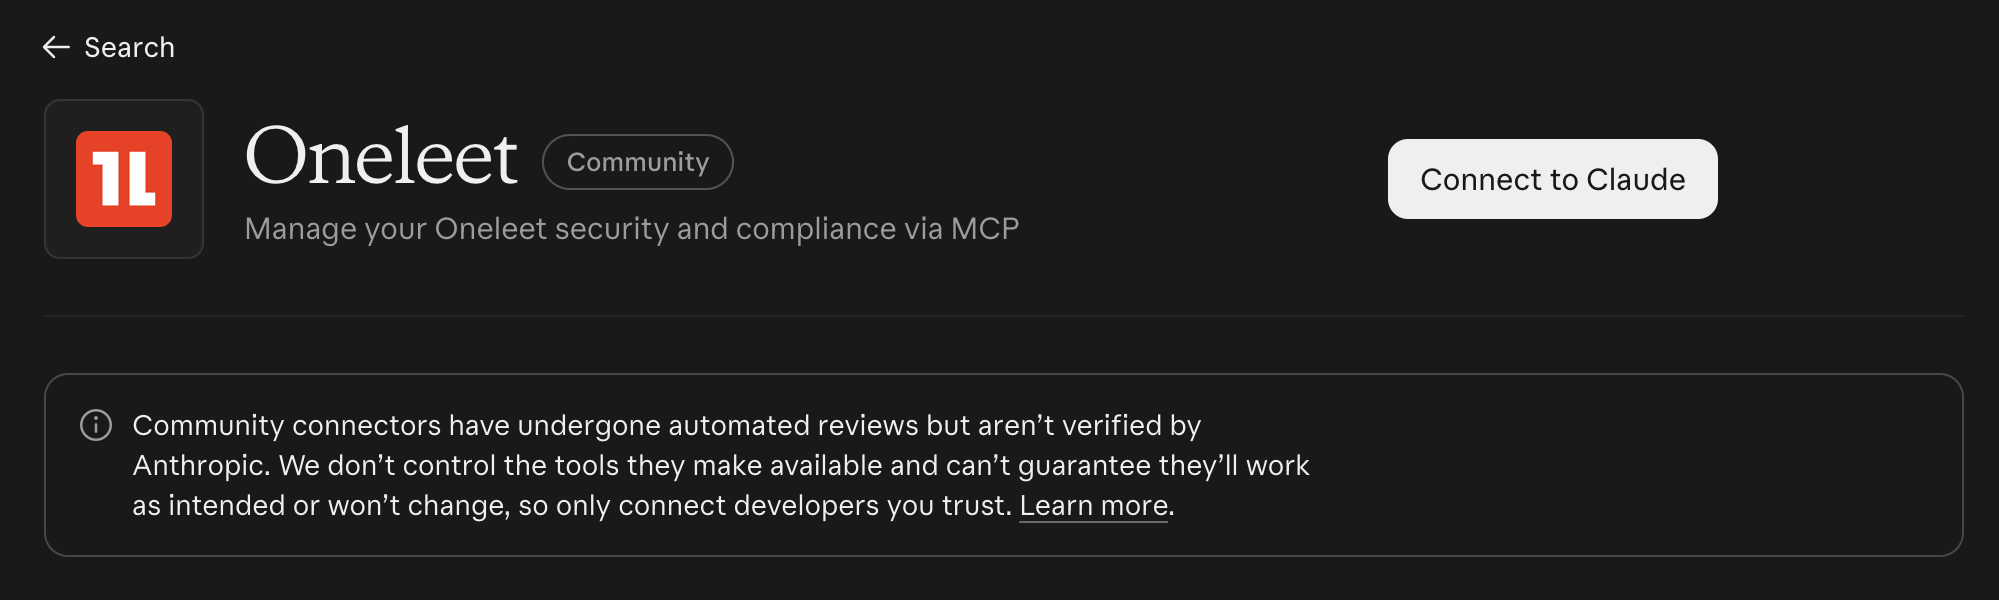
-
Click Connect to Claude and complete the sign-in flow in the browser window that opens.
-
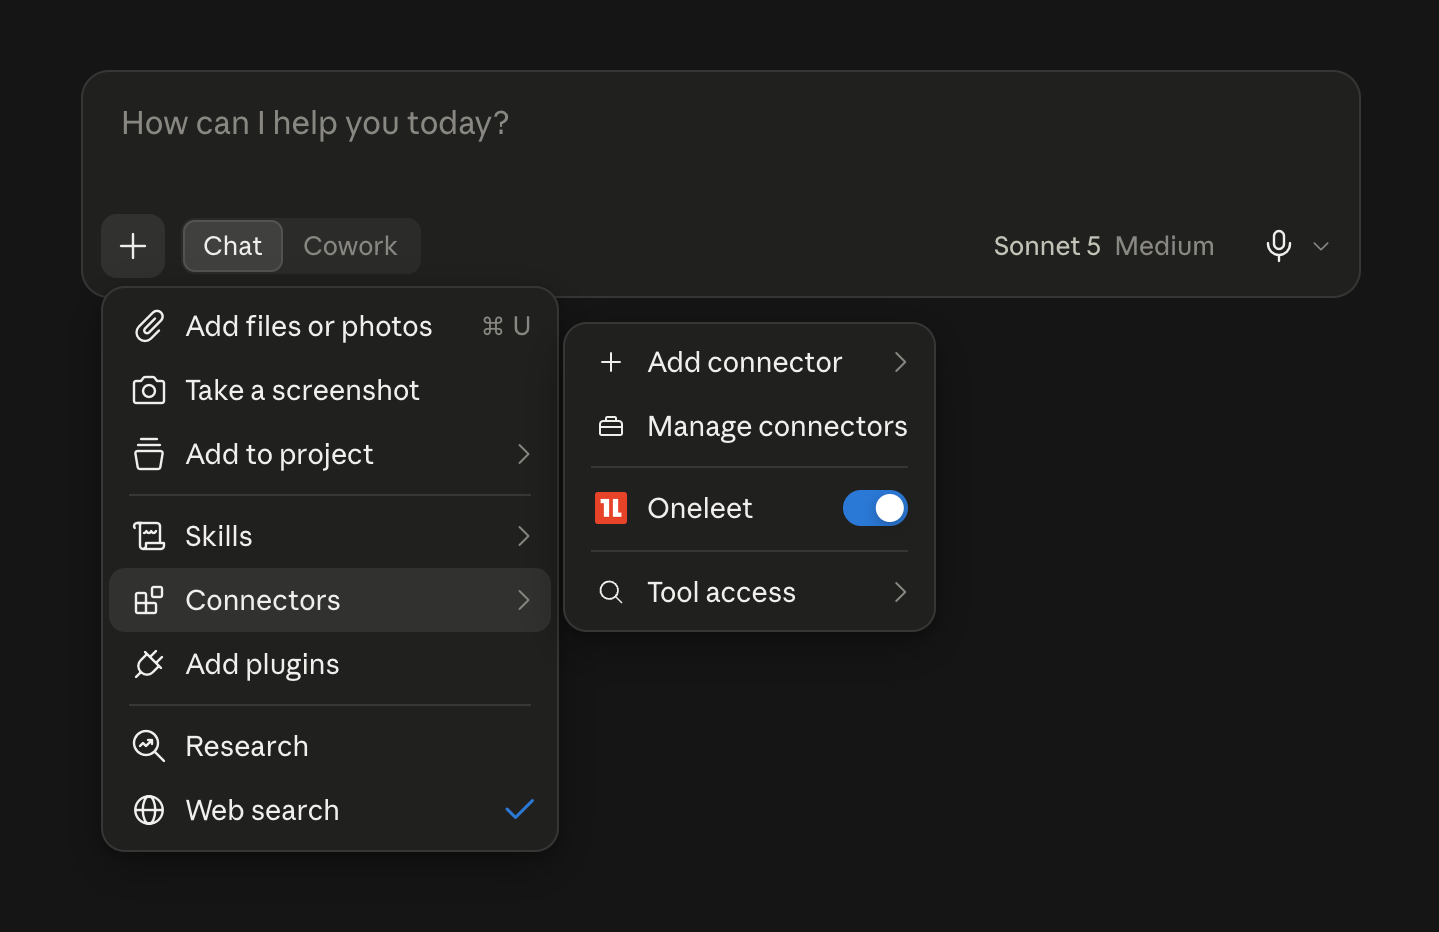
Back in Claude, enable Oneleet in a conversation from the + menu → Connectors, then ask, for example “which of my SOC 2 controls are failing?”.
Add Oneleet as a custom connector
Section titled “Add Oneleet as a custom connector”If Oneleet doesn’t show up in your connector directory, add it as a custom connector instead.
-
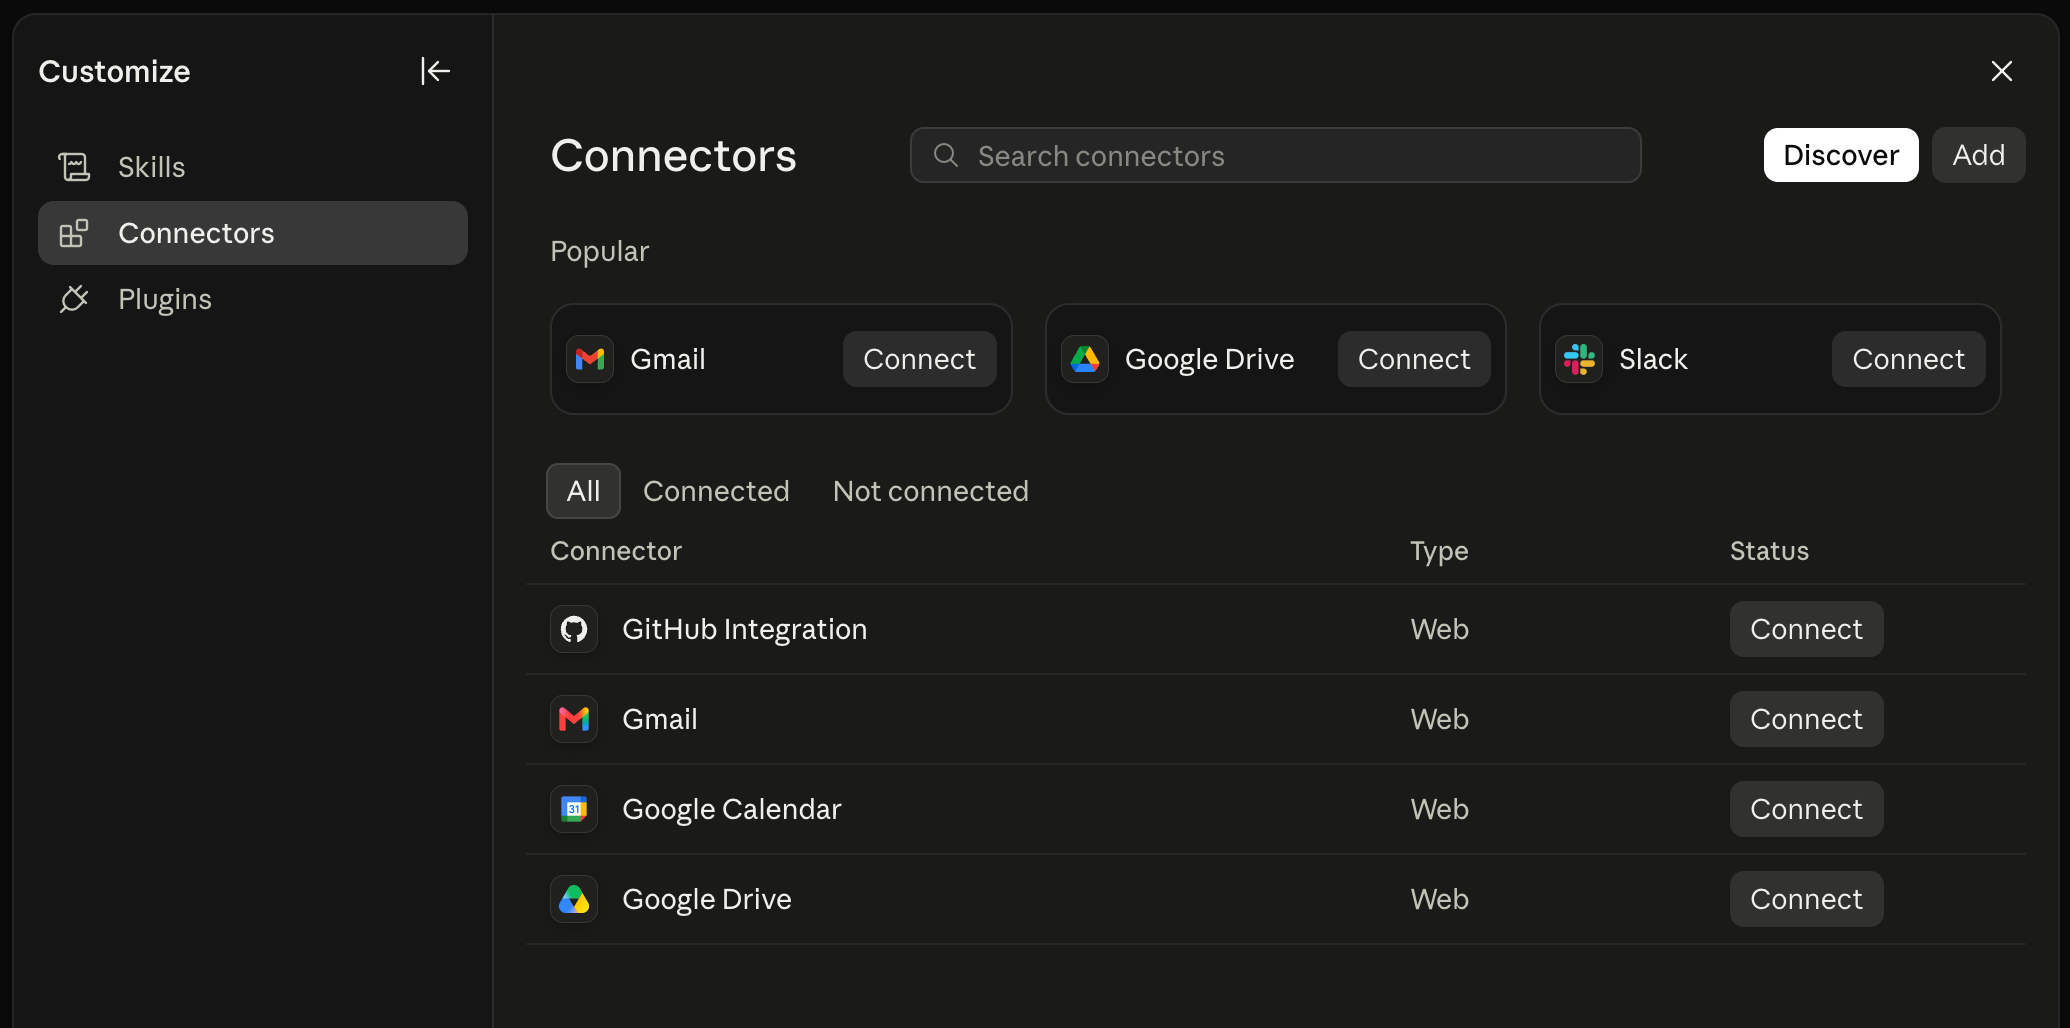
Open Claude’s settings and go to Connectors.
-
Click Add. In the Add custom connector dialog, give it a name such as
Oneleetand enterhttps://api.oneleet.com/mcpas the remote MCP server URL — no client ID or secret is needed. Click Continue.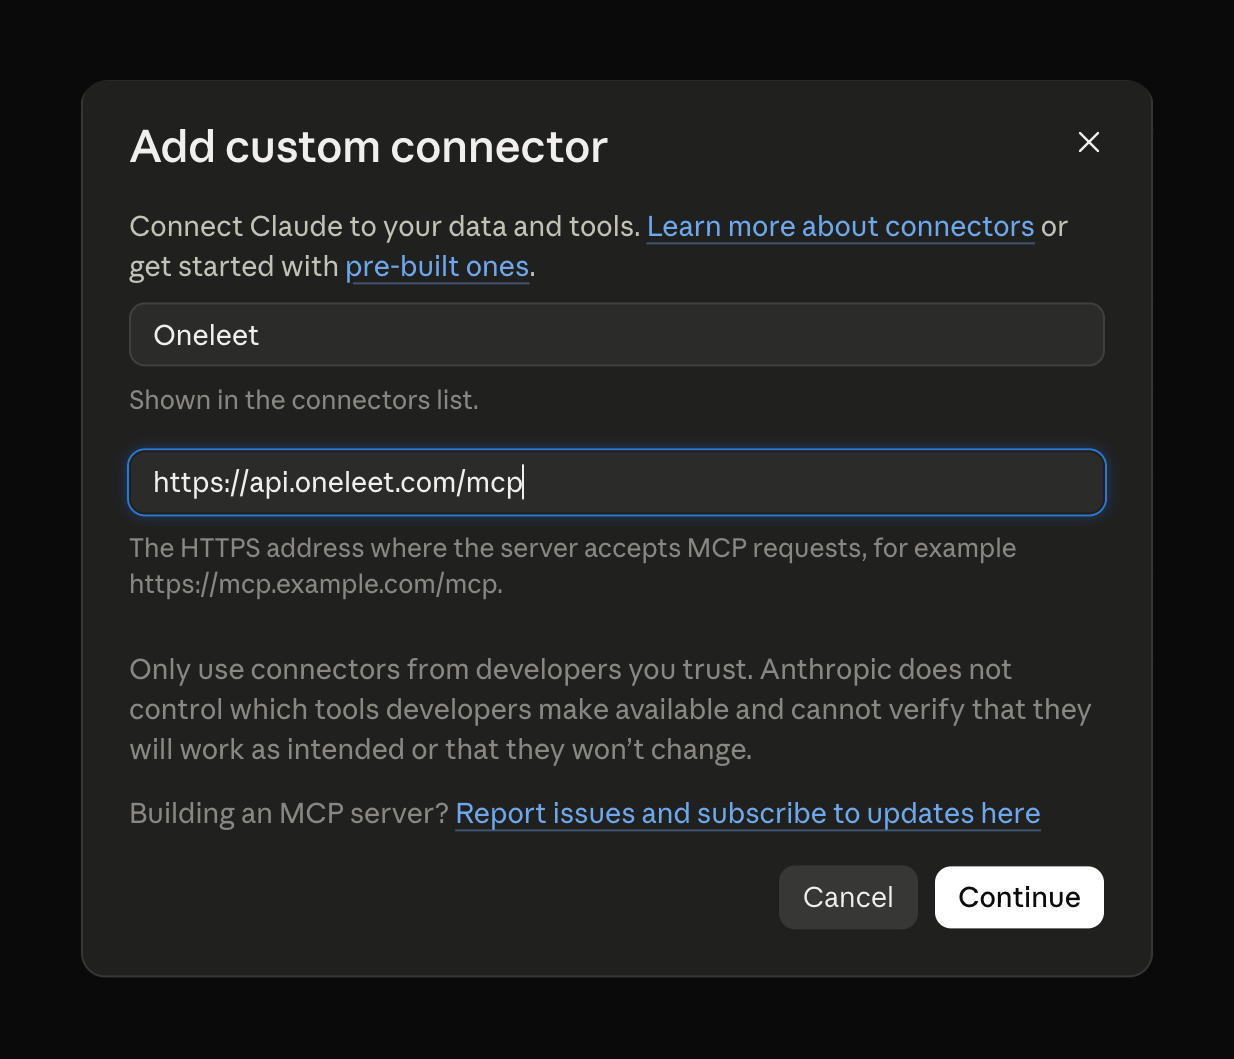
-
The Oneleet connector now appears in your connectors list. Open it to find its Connect button.
-
Click Connect and complete the sign-in flow in the browser window that opens.
-
Back in Claude, enable Oneleet in a conversation from the + menu → Connectors.
Claude Code
Section titled “Claude Code”-
Add the server from your terminal. Use
--scope userto make it available in every project rather than just the current one:Terminal window claude mcp add --transport http --scope user oneleet https://api.oneleet.com/mcpOr add it to
.mcp.jsonin your project root. Don’t add anAuthorizationheader — a static header switches the connection to service key authentication and skips OAuth sign-in entirely:{"mcpServers": {"oneleet": {"type": "http","url": "https://api.oneleet.com/mcp"}}} -
Start
claude, run/mcp, and select oneleet. It’s listed as Needs authentication — choose Authenticate. -
Your browser opens on the Oneleet sign-in page. Complete the sign-in flow. If the browser doesn’t open on its own (for example inside a sandbox or over SSH), Claude Code prints the URL — open it in any browser on the same machine.
-
Once you’re redirected back, the server shows as Connected and its tools are available. Check any time with
claude mcp list:oneleet: https://api.oneleet.com/mcp (HTTP) - ✔ Connected
To sign out, open /mcp, select oneleet, and choose Clear authentication.
To switch workspaces, do the same and then authenticate again — see
Switching workspaces.
ChatGPT
Section titled “ChatGPT”Oneleet is listed in ChatGPT’s plugin directory, so you can add it without entering a server URL or turning on developer mode.
-
Open Oneleet in ChatGPT’s plugin directory. You can also find it in ChatGPT by going to Plugins (
chatgpt.com/plugins) and searching forOneleet.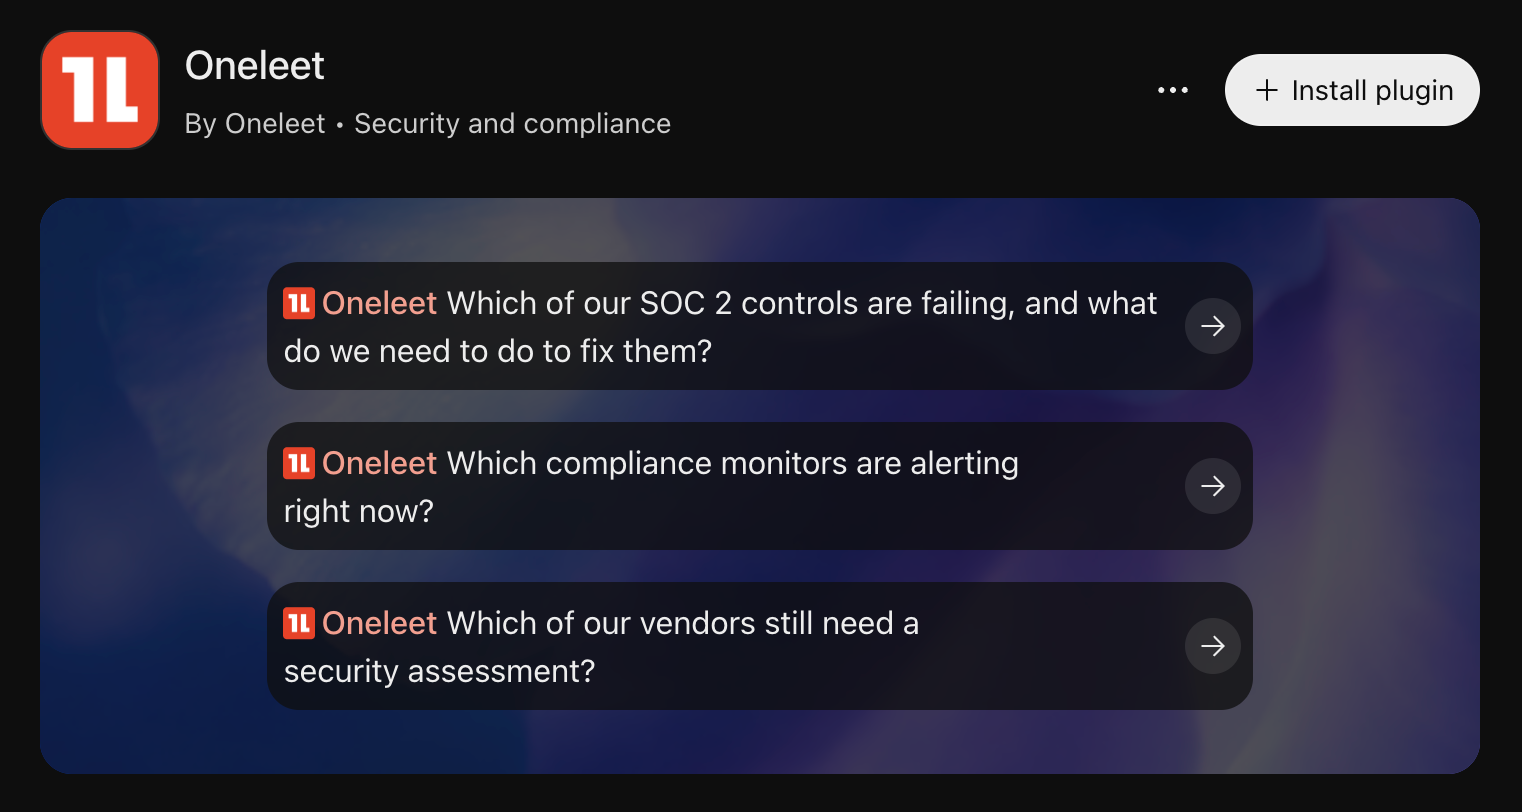
-
Click Install plugin and complete the sign-in flow when ChatGPT opens the Oneleet sign-in page.
-
Start a conversation that uses Oneleet: click one of the example prompts on Oneleet’s plugin page, or type
@Oneleetat the start of your message and then ask, for example “which of our SOC 2 controls are failing?”.Whether ChatGPT asks you before it runs a tool depends on the permissions you’ve set for Oneleet in ChatGPT. Some settings let it run tools that change something, such as uploading evidence or updating a vendor assessment, without asking, and others make it ask before read-only tools too. Check Oneleet’s permissions, as described in OpenAI’s article on app permissions, before you rely on these prompts.
On Business, Enterprise, and Edu plans, a workspace admin controls which plugins members can use. If Oneleet isn’t available to you, ask your ChatGPT workspace admin to enable it.
Add Oneleet in developer mode
Section titled “Add Oneleet in developer mode”If you can’t add Oneleet from the plugin directory, connect it as a custom plugin through developer mode, available on Pro, Plus, Business, Enterprise, and Edu plans on the web. On Business, Enterprise, and Edu plans a workspace admin may need to enable developer mode first, and OpenAI limits some plans to read-only tools for custom servers — see OpenAI’s developer mode help article for the current plan limits.
-
Open Settings → Security and login and turn on Developer mode.
-
Go to Plugins (
chatgpt.com/plugins) and click +. In the New Plugin form, enter a name such asOneleet, set the Server URL tohttps://api.oneleet.com/mcp, and set Authentication to OAuth. Leave Advanced OAuth settings untouched — everything is discovered automatically. Acknowledge the custom-server notice by ticking I understand and want to continue, then click Create.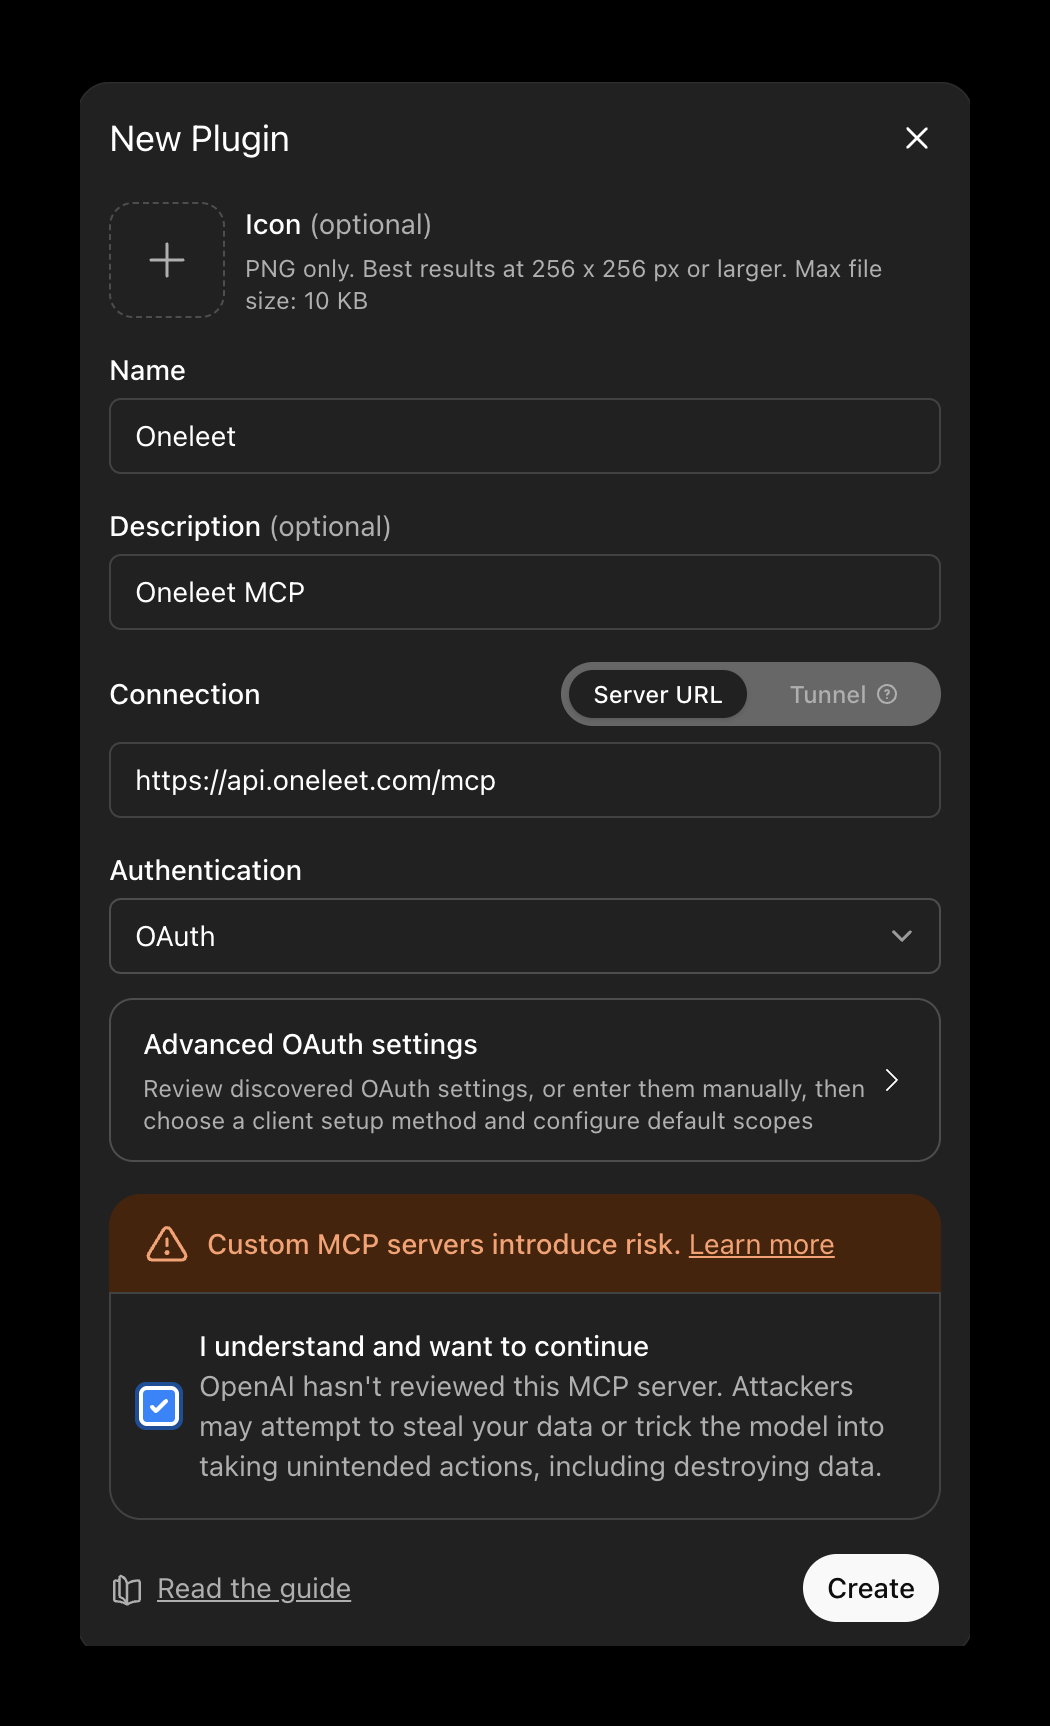
-
Complete the sign-in flow when ChatGPT opens the Oneleet sign-in page. Once you’re back, wait for ChatGPT to finish scanning the available tools.
-
In a new conversation, open the + menu → Developer mode and select Oneleet.
The Codex CLI and IDE extension share one configuration.
-
Add the server and sign in:
Terminal window codex mcp add oneleet --url https://api.oneleet.com/mcpcodex mcp login oneleet -
Your browser opens on the Oneleet sign-in page — complete the sign-in flow. When it finishes, the Oneleet tools are available in your next Codex session (
codex mcp listshows the configured server).
Cursor
Section titled “Cursor”-
Add the server to
~/.cursor/mcp.json(available in every project) or.cursor/mcp.jsonin your project root. Configure only the URL — don’t add anAuthorizationheader, which would switch the connection to service key authentication:{"mcpServers": {"oneleet": {"url": "https://api.oneleet.com/mcp"}}} -
Open Cursor Settings → Tools & MCP. The Oneleet server is listed as Needs authentication — click Connect.
-
Your browser opens on the Oneleet sign-in page. Complete the sign-in flow; once you’re sent back to Cursor, the Oneleet tools appear under the server and are available in chat.
Devin connects to Oneleet as a custom MCP server on app.devin.ai. Adding one needs Devin’s Manage MCP Servers permission, so if you don’t see Add custom MCP, ask an admin of your Devin organization to add the server. After that, each member connects their own Oneleet account.
-
In Devin, go to Customize → MCPs, open Add MCP, and choose Add custom MCP.
-
Name the server
Oneleet, set the transport type to HTTP, enterhttps://api.oneleet.com/mcpas the Server URL, and set Authentication method to OAuth. -
Under OAuth credentials, enter Oneleet’s client ID for Devin and leave the client secret empty:
tpc_f5d1bwUaJW7Sh25paqtLoS -
Set Access to Personal and click Save.
-
Click Connect and complete the sign-in flow in the browser window that opens. Back in Devin, click Test tools to check that the Oneleet tools are listed. Connect before you start a Devin session that should use Oneleet.
If your organization uses a dedicated Devin deployment rather than app.devin.ai, sign-in stops with a Callback URL mismatch error, because Devin calls back to your deployment’s own address. Send the OAuth callback URL shown under OAuth credentials in Devin to your Oneleet representative, and we’ll add it.
Google Antigravity
Section titled “Google Antigravity”-
In Antigravity, add a remote MCP server named
oneleetwith the URLhttps://api.oneleet.com/mcp. Configure only the URL. Don’t add anAuthorizationheader or any credentials. -
When Antigravity opens the Oneleet sign-in page, complete the sign-in flow. Once you’re sent back to Antigravity, the Oneleet tools are available to its agents.
-
In Grok on the web, add a custom connector with
https://api.oneleet.com/mcpas its server URL. No client ID or secret is needed. -
Complete the sign-in flow when Grok opens the Oneleet sign-in page. The consent screen names the client as Cursor, because Grok signs in with Cursor’s registration. That’s expected, but it means Grok and Cursor share one workspace (see One workspace at a time).
Other MCP clients
Section titled “Other MCP clients”Oneleet only accepts sign-in from MCP clients we’ve registered. A client that isn’t listed above fails sign-in with an unknown client error, even if it implements the MCP authorization specification. To use one, ask your Oneleet representative to register it, and connect with a service key in the meantime.
The sign-in flow
Section titled “The sign-in flow”Whichever client starts it, the browser part of connecting looks like this.
-
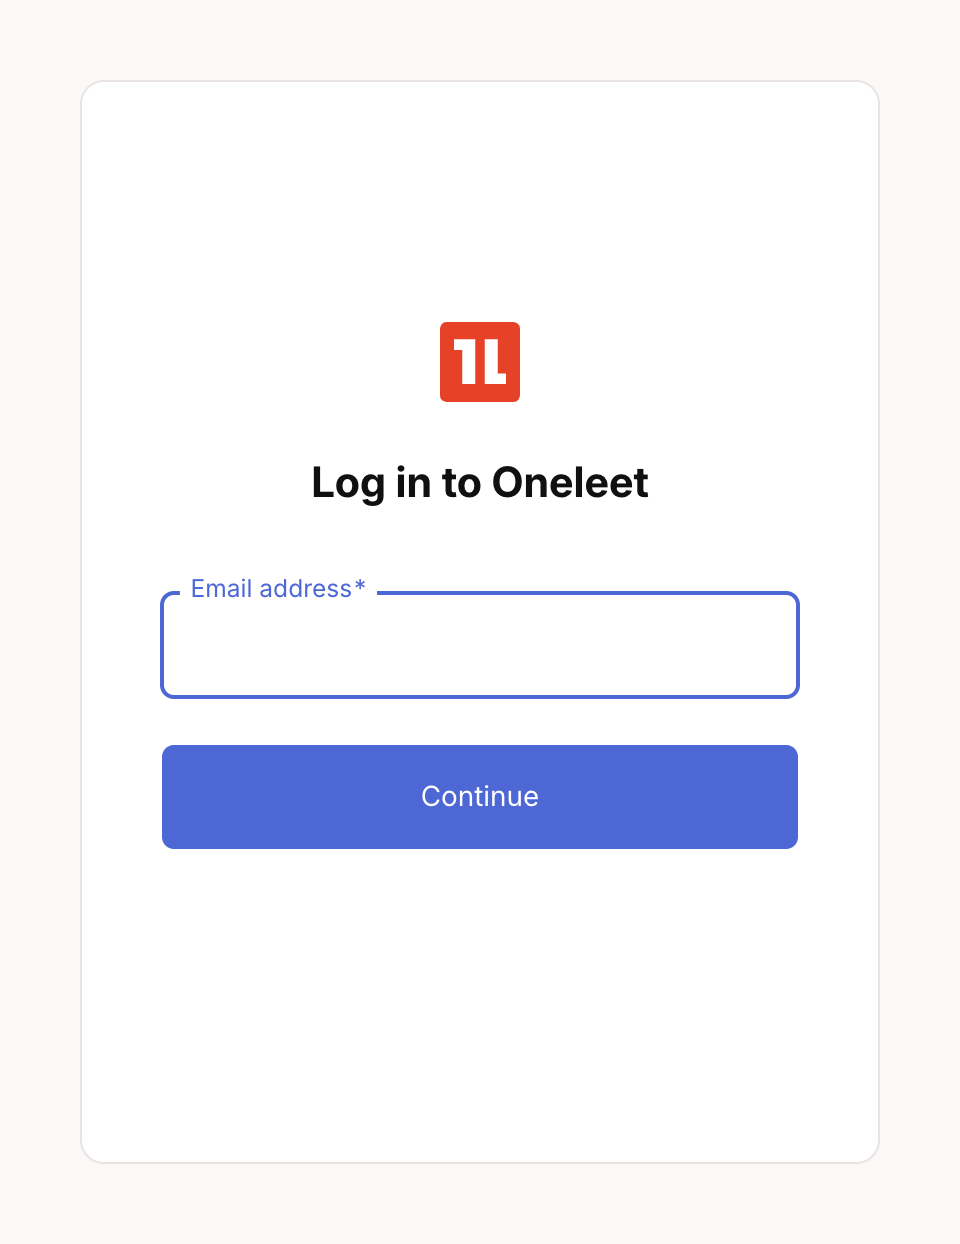
The client opens the Oneleet sign-in page. Enter the email address of your Oneleet account and click Continue, or click Continue with Google if you log in to Oneleet with Google. Use the same account you log in to Oneleet with — the connection is matched to your account by email.
-
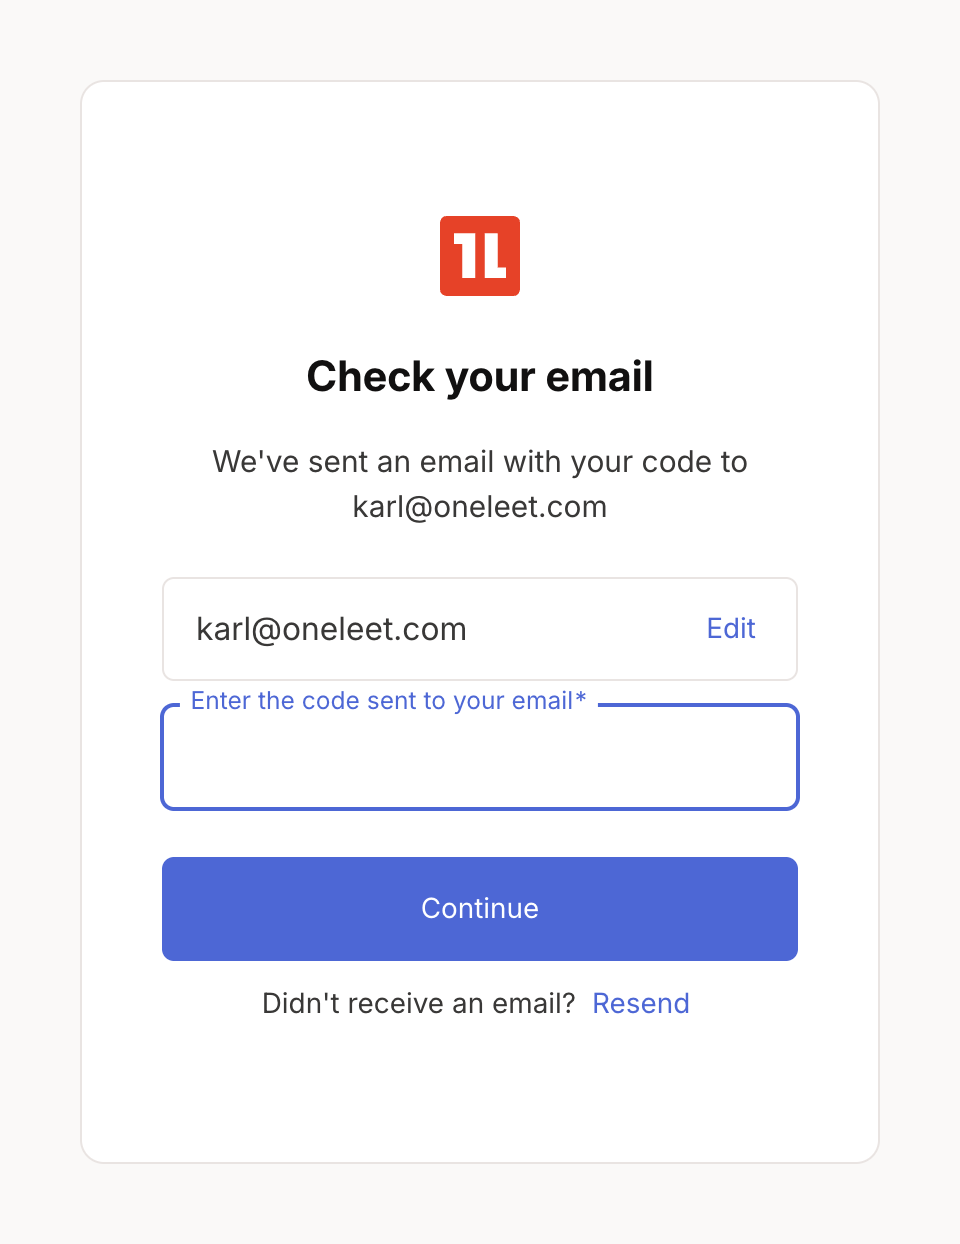
If you entered your email address, enter the one-time code that Oneleet emails you. With Continue with Google, you sign in with Google instead. If you recently logged in to Oneleet in this browser, both of these steps may be skipped.
-
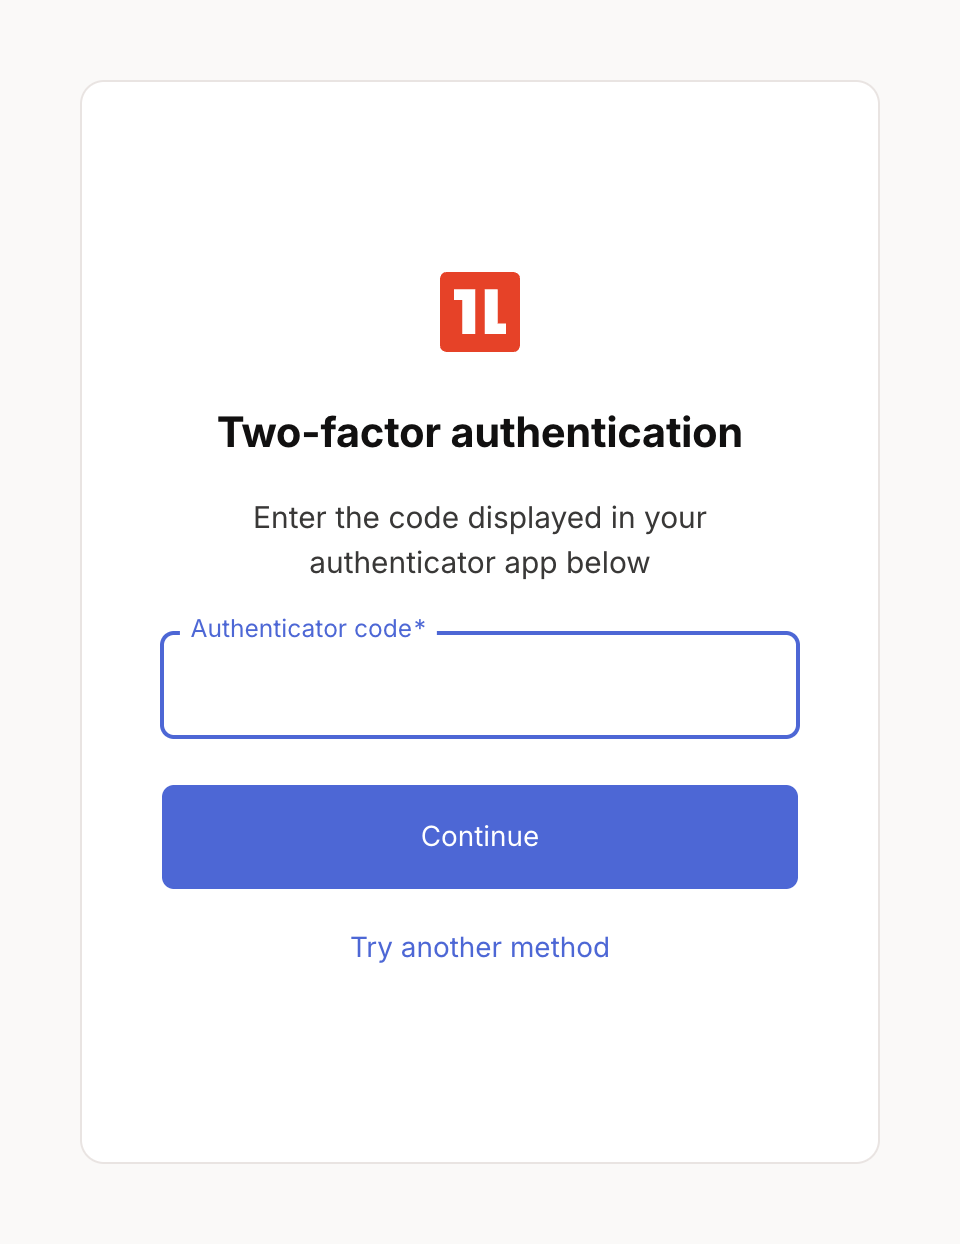
If your Oneleet account has two-factor authentication set up, enter the code from your authenticator app.
-
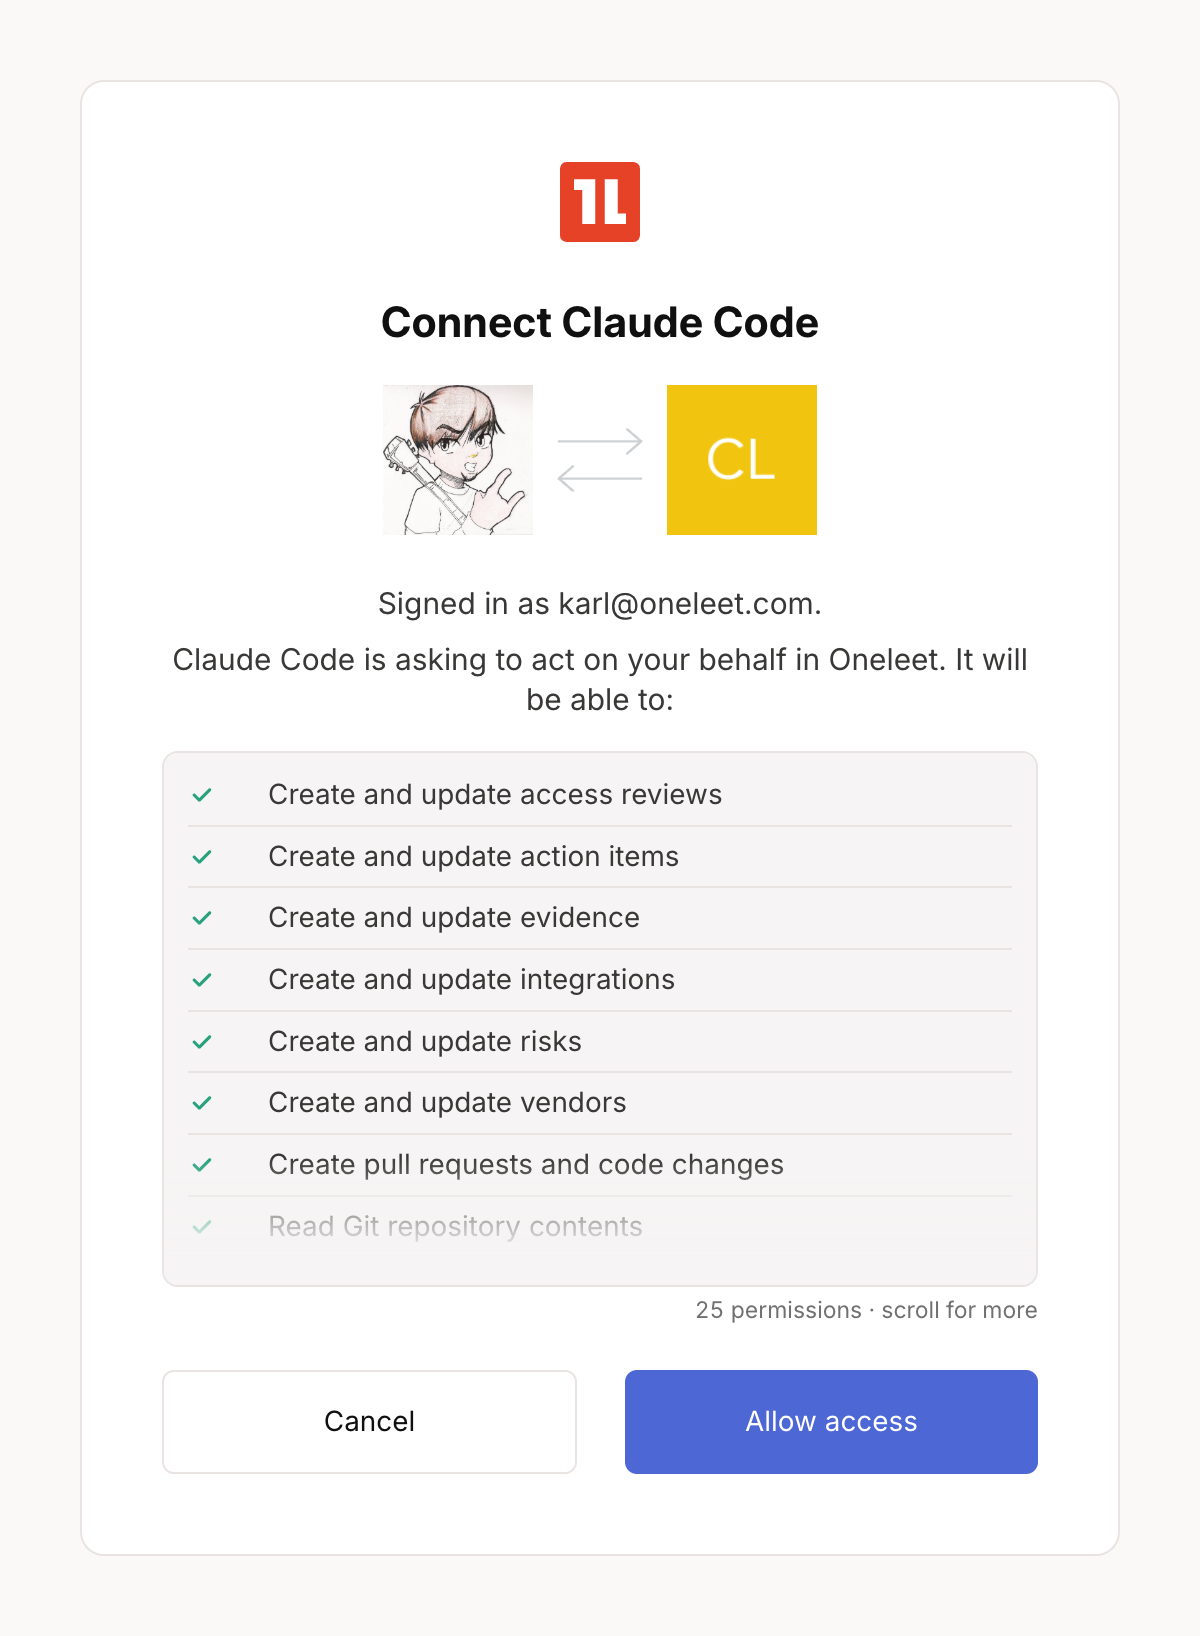
Review what the assistant is asking to access and click Allow access. The list shows every permission the assistant may use — your actual access is always limited to what your role in the workspace allows (see How access is enforced). Cancel aborts the connection without granting anything.
-
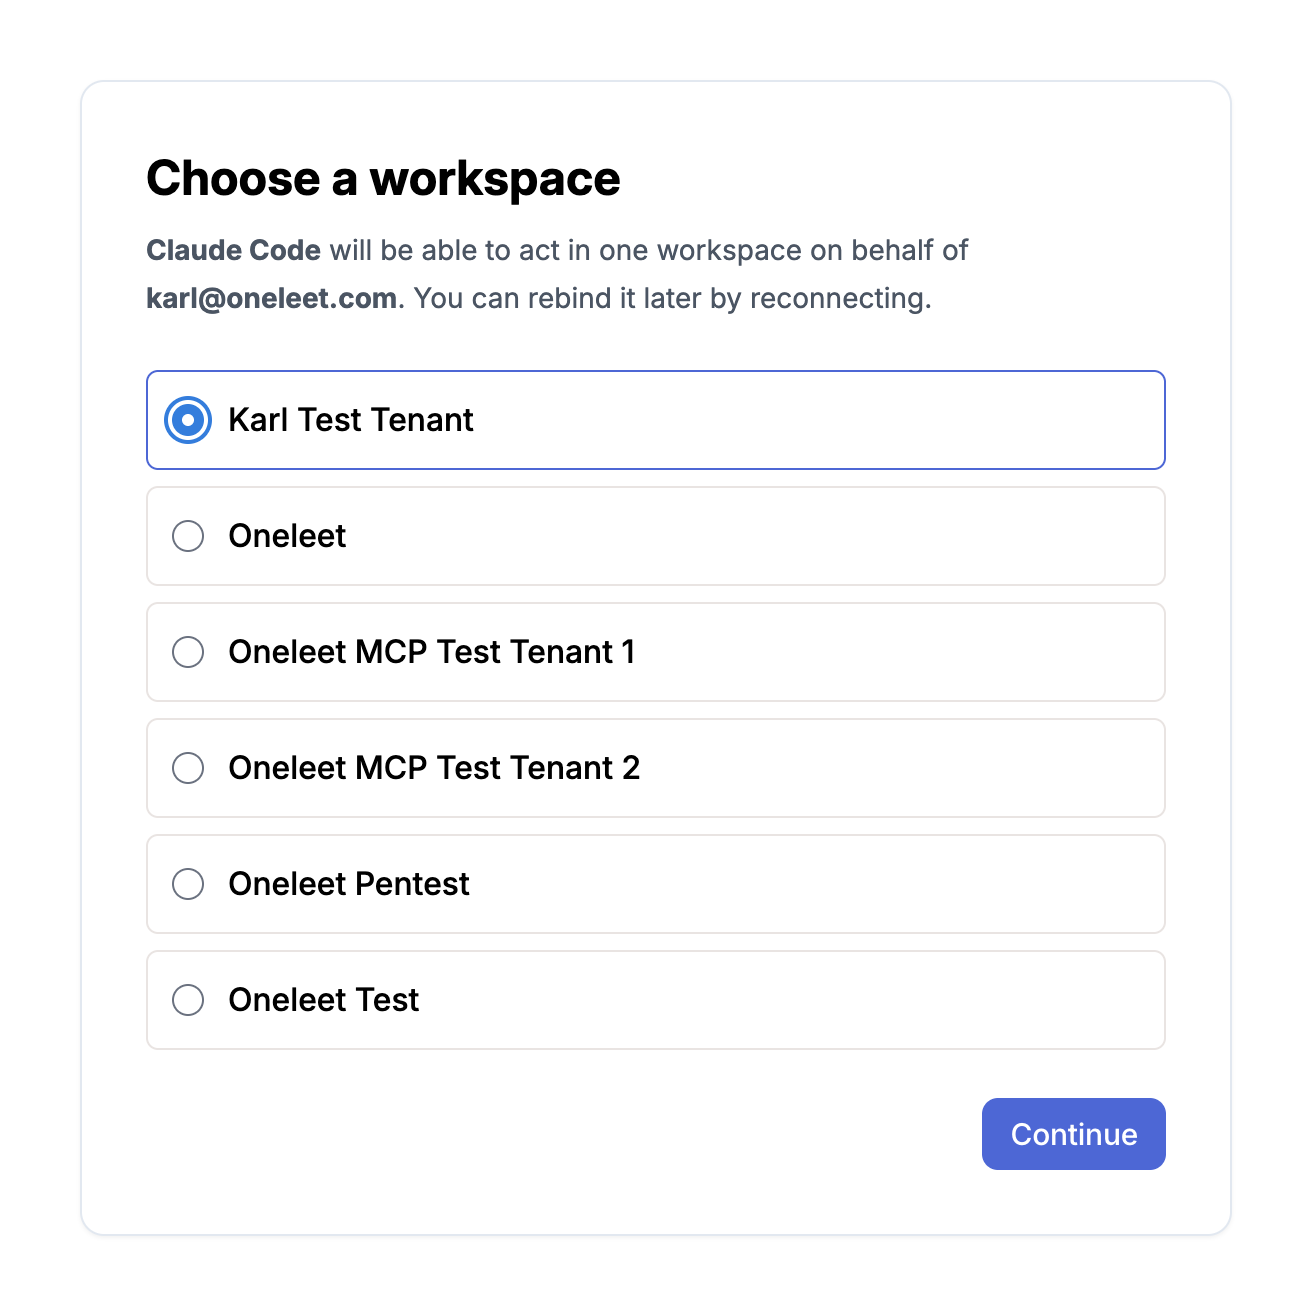
If you’re a member of more than one workspace, choose the one this assistant should work in and click Continue. A connection is bound to exactly one workspace; if you belong to only one, it is selected automatically and this step is skipped.
-
You’re sent back to the client, which is now connected. You can close the browser window.
Switching workspaces
Section titled “Switching workspaces”Each connection works in one workspace. To point an assistant at a different workspace, disconnect and connect it again (for example Clear authentication followed by Authenticate in Claude Code, or Disconnect followed by Connect on the Oneleet connector in Claude). The sign-in flow runs again and the workspace chooser is shown with your previous choice preselected — pick the new workspace and continue.
How access is enforced
Section titled “How access is enforced”Connecting with OAuth never grants an assistant more than you have yourself.
- The assistant acts as you. Every call is authorized as your user in the workspace you chose, so it inherits your workspace role and any organization roles you hold. Changes to your roles apply to the assistant on its very next call — there is nothing to reconnect.
- Two limits, both must pass. A call succeeds only if it is covered by the permissions you allowed on the consent screen and by your own role. A read-only member’s assistant can’t create evidence no matter what it was allowed to ask for, and an admin’s assistant can’t do anything the admin didn’t allow.
- The tool list follows what you allowed. The assistant is shown only the tools covered by the permissions you allowed on the consent screen. Your role is checked when a tool is called, so a listed tool can still be denied if your role doesn’t include it.
- One workspace per connection. The workspace is fixed when you connect. An assistant can never reach another workspace, even if you’re a member of it, without you reconnecting and choosing it.
- Membership is checked on every call. If you’re removed from the workspace, the connection stops working immediately and stays broken until it’s reconnected — by a member. If your workspace access is removed but you remain in the workspace as an employee, the connection keeps working with an employee’s permissions only.
- Verified identity. Sign-in requires a verified email address that belongs to an existing Oneleet workspace member. An address that isn’t a member of any workspace can’t complete the flow.
- Short-lived credentials. Access tokens expire after 15 minutes and are renewed silently by the client while the connection is active. Disconnecting in the client discards them. Nothing is shown to you that could be copied into another tool — there is no secret to leak.
- Attributed to you. Anything the assistant creates or changes shows up under your name, the same as if you had done it in the dashboard.
Troubleshooting
Section titled “Troubleshooting”| What you see | What it means |
|---|---|
| Your account isn’t a member of any workspace | The email address you signed in with isn’t a member of a workspace. Sign in with the address your Oneleet invitation was sent to, or ask a workspace admin to invite you, then connect again. |
| This connection attempt expired on the Choose a workspace page | The workspace chooser was left open too long — sign-in sessions are only valid for a few minutes. Restart the connection from your client. |
| Nothing to connect | The Choose a workspace page was opened directly rather than from a sign-in started by an MCP client. Start the connection from the client. |
| This connection has no Oneleet workspace bound to it. | The client tried to renew a connection that was never bound to a workspace. Disconnect and connect again from the client to choose one. |
| You are no longer a member of that workspace. | Your membership was removed between opening the chooser and continuing. Pick another workspace, or ask an admin to re-add you. |
| The client reports it needs authentication, or tools fail after they used to work | Your connection could not be renewed — typically because you were removed from the workspace, or your session with Oneleet was revoked. Authenticate again; if that still fails, check with a workspace admin. |
| A tool call is denied although the assistant was allowed to use it | Your own role doesn’t include that permission. The consent screen lists what the assistant may do; your role decides what it can do. Ask an admin for the permission if you need it. |
| An error page saying Unable to process redirect callback right after the workspace step | Oneleet couldn’t finish the sign-in for the way your account is set up. Connect with a service key if your client supports one, and tell your Oneleet representative so they can get your account fixed. |
| Sign-in fails with unknown client or not authorized | Oneleet doesn’t recognize the MCP client. If it’s one of the supported clients above, a recent update to the client may have changed how it identifies itself. Connect with a service key for now, and tell your Oneleet representative which client and version you’re using. |
| Callback URL mismatch when connecting from Devin | Your organization uses a dedicated Devin deployment that we haven’t set up sign-in for yet. See Devin for what to send us. |
| The browser never opens (Claude Code, Codex) | Copy the sign-in URL the client prints into a browser on the same machine. The redirect back to the client is to localhost, so it must be a browser on the machine running the client. |
| The assistant suddenly works in a different workspace than the one you connected it to | The same assistant was connected to another workspace — for example through a second server entry. An assistant can be connected to one workspace at a time (see Switching workspaces). Reconnect and choose the workspace you want. |
OAuth sign-in vs. service keys
Section titled “OAuth sign-in vs. service keys”| Topic | OAuth sign-in | Service key |
|---|---|---|
| Who sets it up | Any workspace member, for themselves | Workspace admins |
| Identity | You — calls are attributed to your account | The key — calls are attributed to the key |
| Permissions | What you allowed on the consent screen, capped by your own role (system or organization roles) | Exactly the scopes granted to the key, independent of any user |
| Workspace | One at a time per assistant, chosen at sign-in | Fixed to the workspace the key was created in |
| Credentials | Short-lived tokens managed by the client; nothing to copy or store | A long-lived secret you must store safely; shown once at creation |
| Ends when | You disconnect, or you’re no longer a member of the workspace | The key expires or an admin revokes it |
| Best for | Hosted assistants (Claude on the web, ChatGPT, Devin, Grok) and personal use in Claude Code, Codex, Cursor, or Antigravity | Scripts, CI, shared automations, and clients without OAuth support (curl, etc.) |
| Available tools | The same MCP tools and public API either way | Same |